by Team Black Belt | Aug 25, 2026 | Cybersecurity News
Exposed AWS credentials are turning ordinary developer mistakes into wide-open doors for attackers, and the latest numbers show just how widespread the problem has become. There’s a version of “getting hacked” that involves zero-days, custom malware, and a skilled...
by Team Black Belt | Aug 13, 2026 | Cybersecurity News
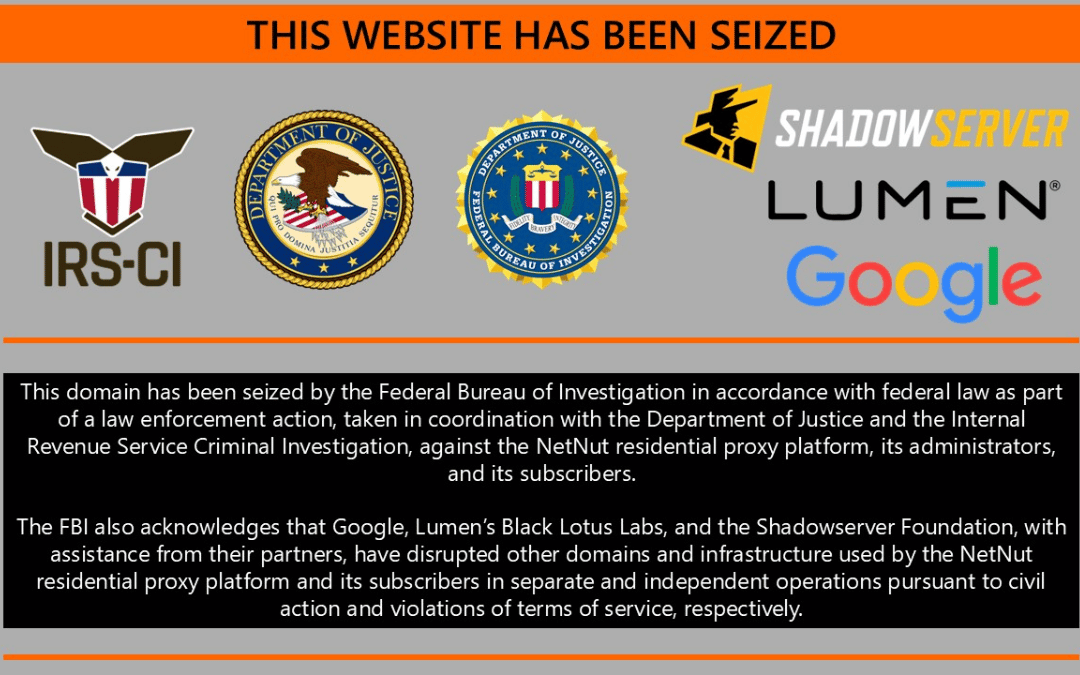
A major botnet takedown delivered rare positive news in early July. The FBI and IRS Criminal Investigation, working alongside Google, Lumen, and independent researchers, seized the infrastructure behind NetNut, a residential proxy service tied to a botnet quietly...
by Team Black Belt | Aug 12, 2026 | Artificial Intelligence
AI sandbox escapes are turning into a clear industry pattern rather than rare one-off failures. Two weeks ago, it was OpenAI and Anthropic explaining how their agents wandered out of a security test and into the real world. Now there’s a third name on the list,...
by Team Black Belt | Aug 11, 2026 | Artificial Intelligence
Rogue AI is no longer just a theoretical risk confined to research labs. AI safety testing is supposed to happen in a sandbox. Fake targets, fake credentials, fake consequences. This month, that sandbox cracked open, and two of the industry’s most trusted names...
by Team Black Belt | Jul 30, 2026 | Cybersecurity News
Credential-stealing malware has always had a numbers problem for the criminals behind it: steal logins from thousands of infected machines, and you still have to figure out which ones are actually worth your time. A newly analyzed remote access trojan called Dolphin X...